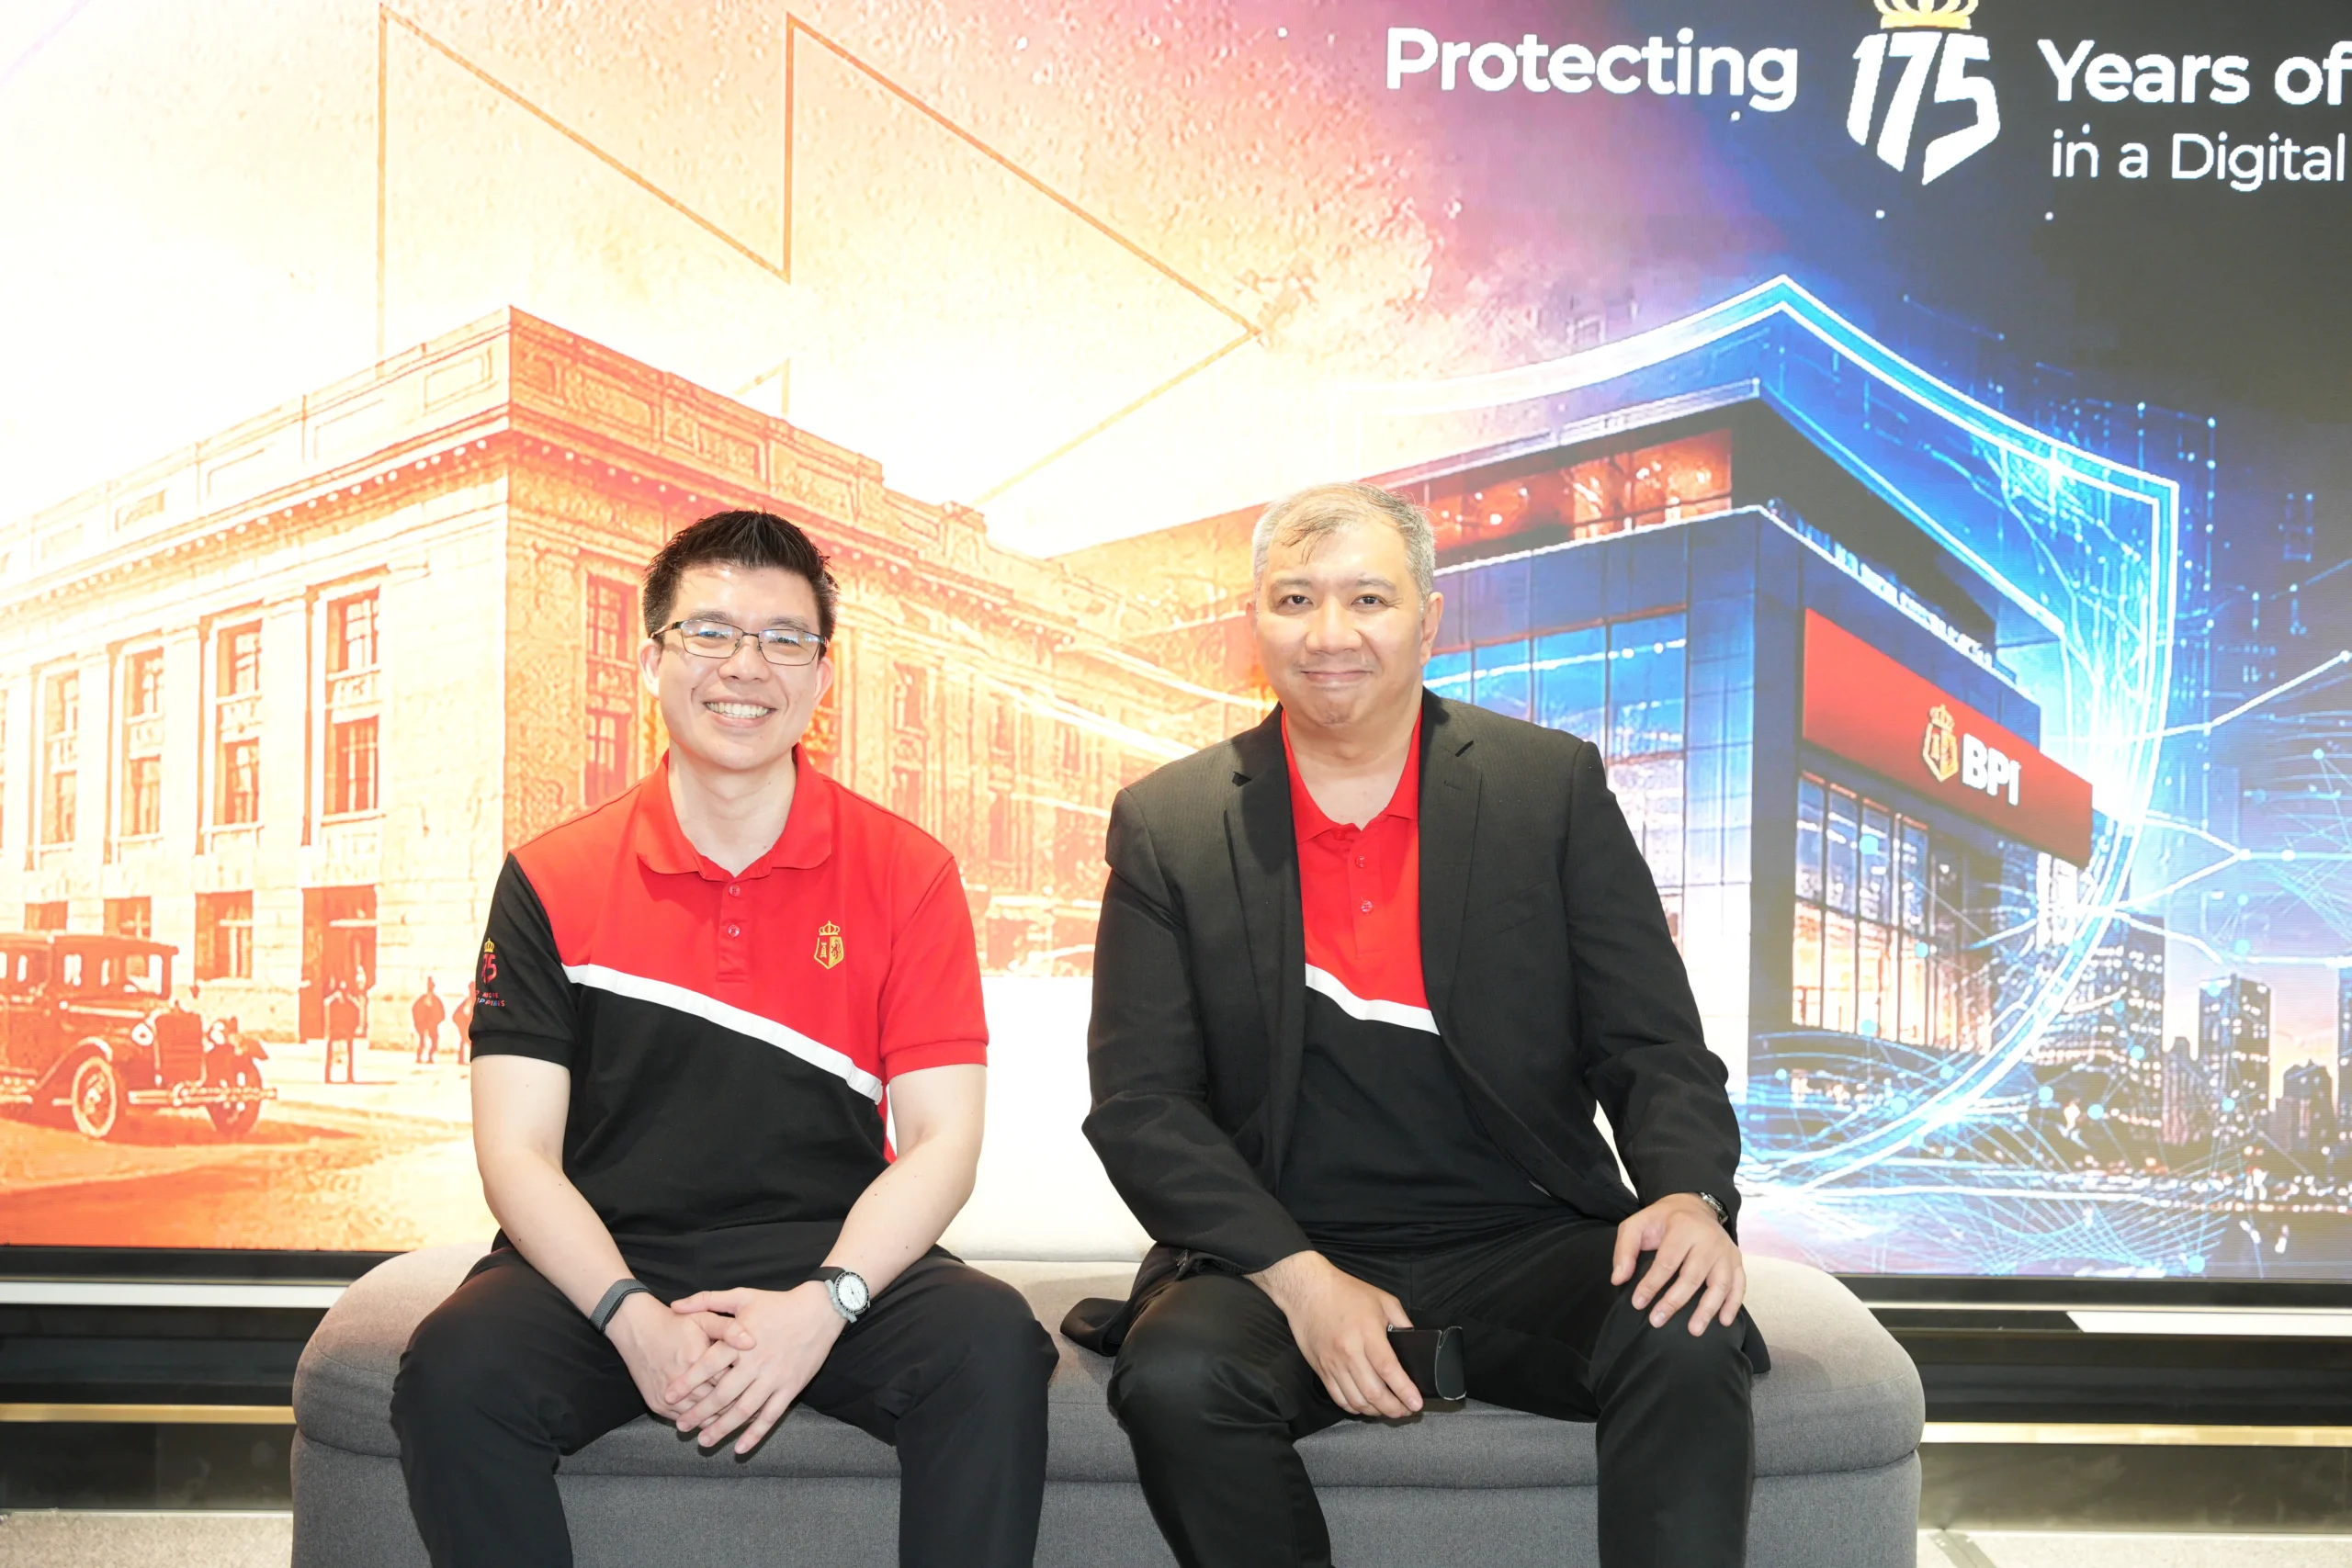
The Bank of the Philippine Islands (BPI) is strengthening its cybersecurity measures and customer education efforts as it marks 175 years of serving Filipinos. The bank says its approach combines transaction safeguards with efforts to help customers recognize scams and make safer decisions while banking online.
BPI digital banking security is being positioned as an ongoing responsibility rather than a one-time response to incidents. Jon Paz, BPI’s Head of Enterprise Information Security and Fraud Risk Management, said financial institutions need to anticipate risks, continuously improve their defenses and work with the broader ecosystem to address fraud.
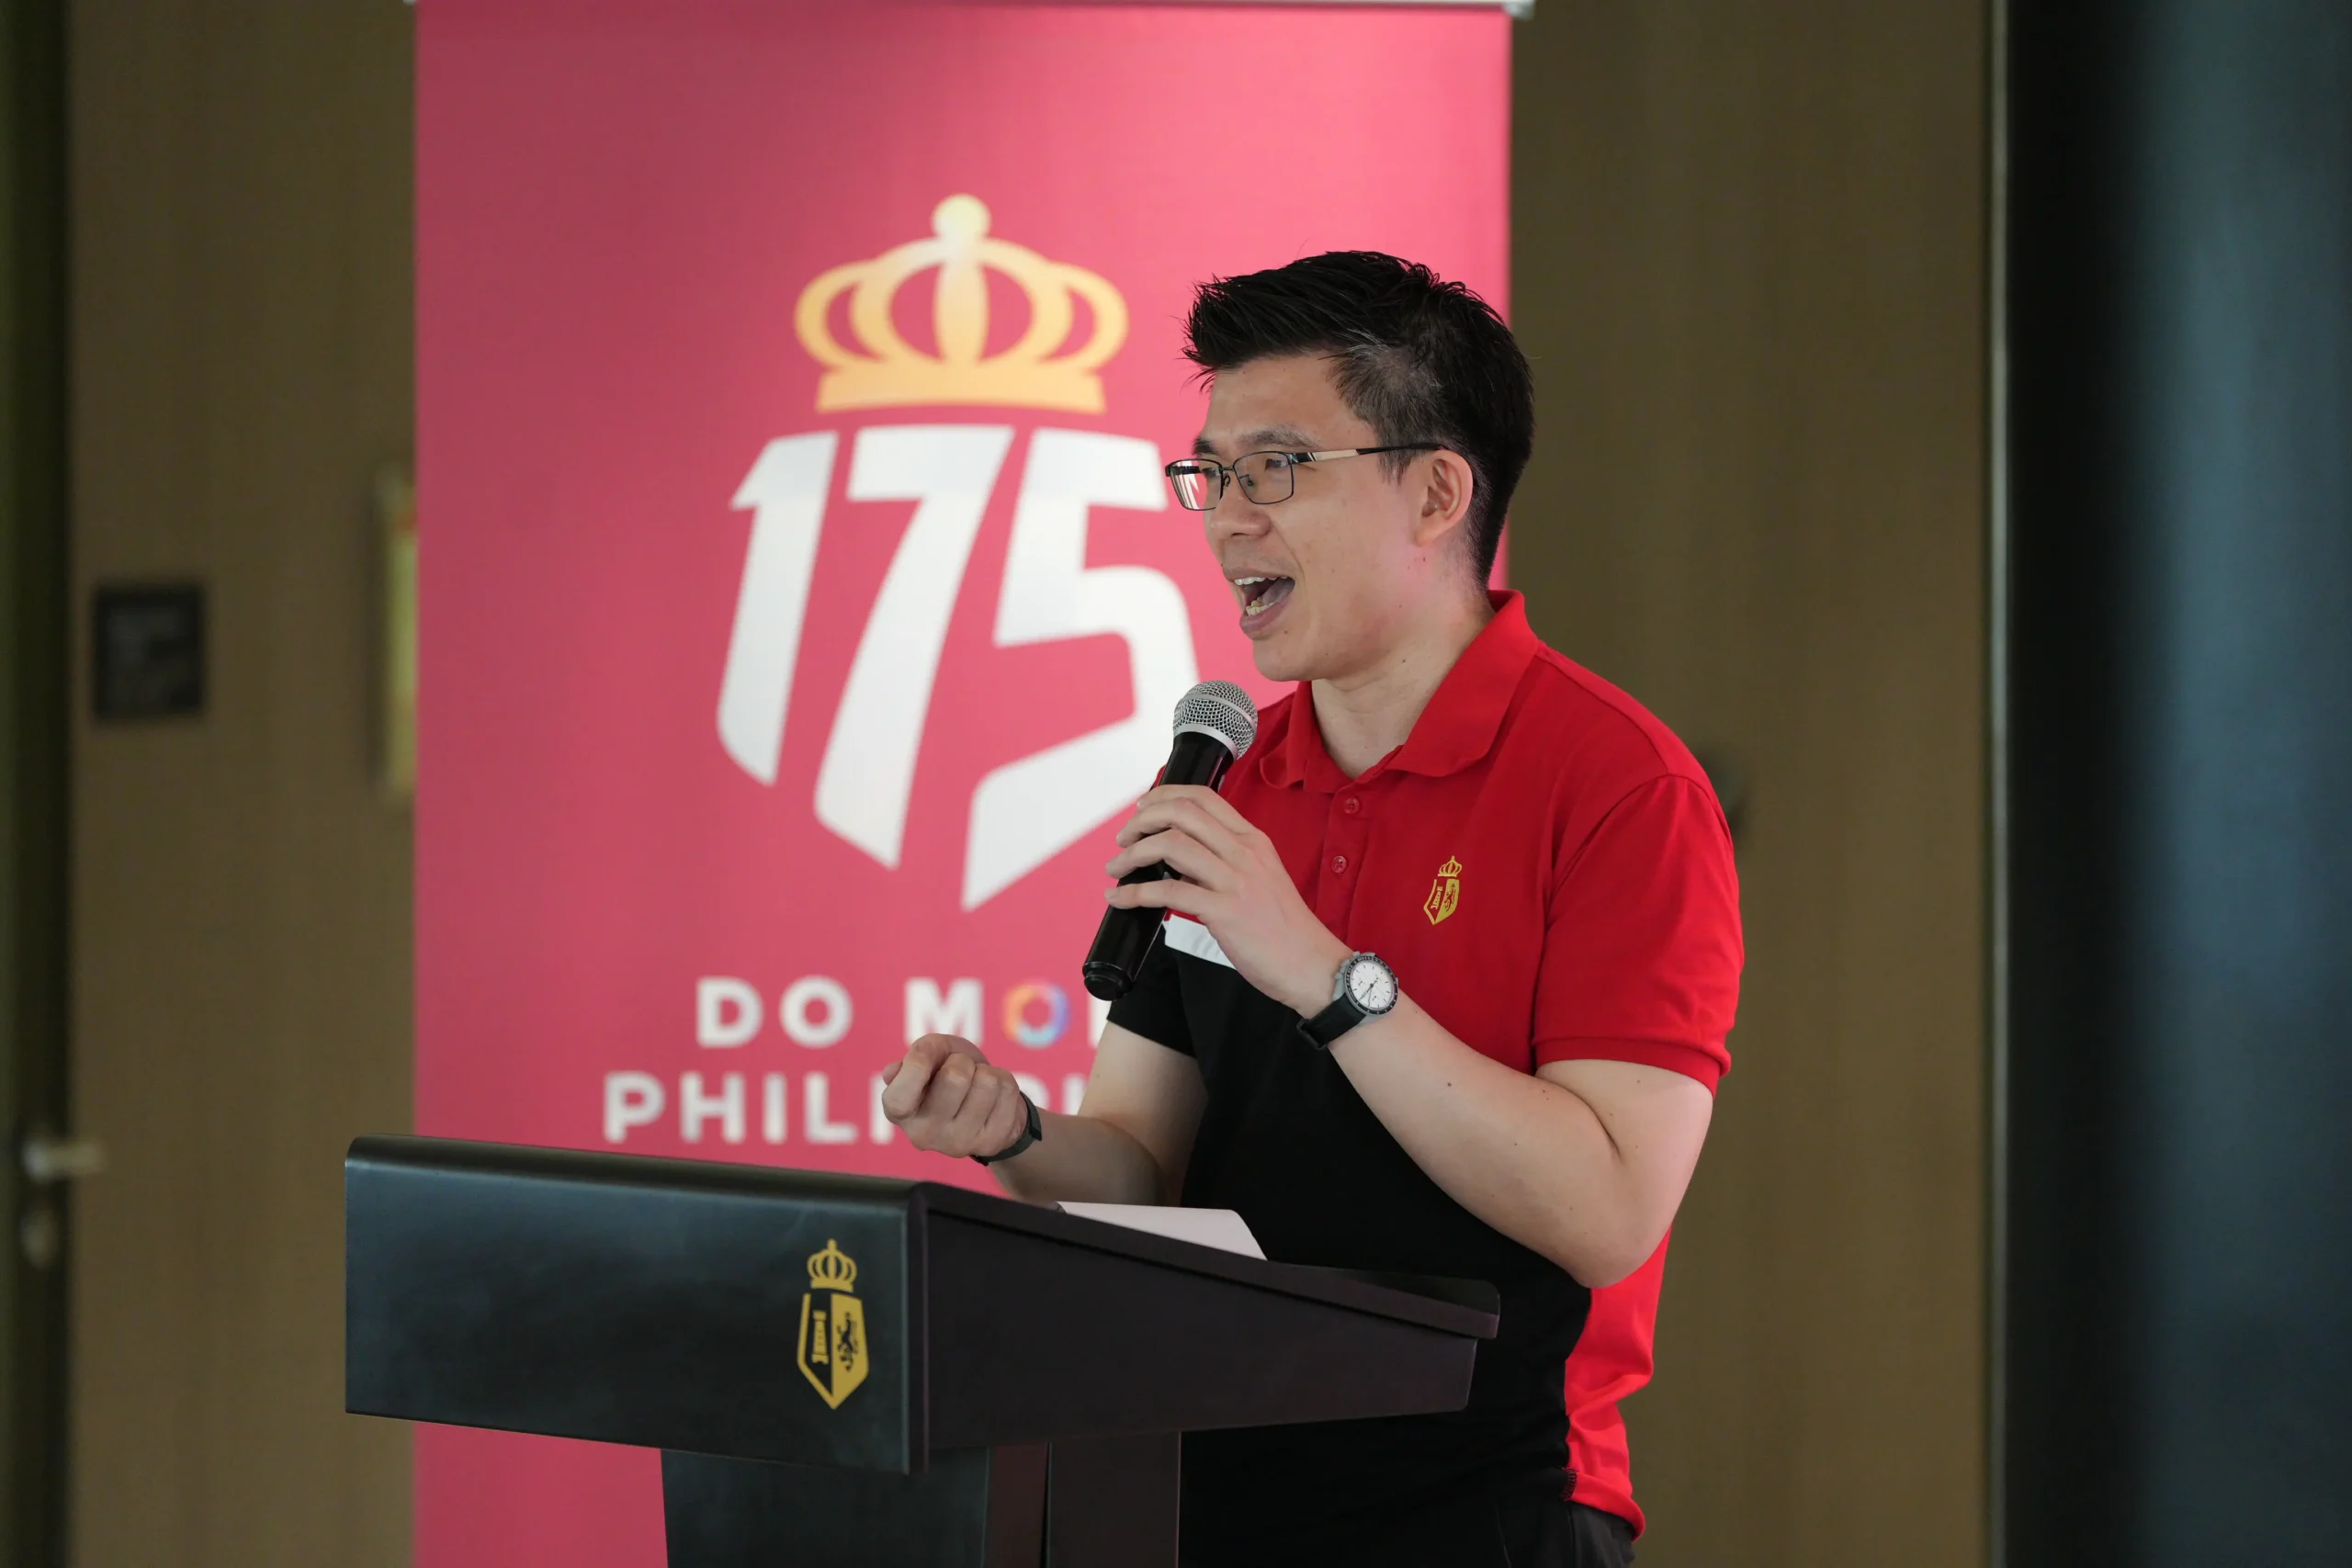
“Cybersecurity is not about responding to threats after they happen. It requires financial institutions to anticipate risks, continuously strengthen their defenses, and work together with the broader ecosystem to address fraud. As digital banking evolves, protecting customers means making security an ongoing priority, not a one-time effort,” Paz said.
The bank cited industry data showing that social engineering schemes account for nearly 39% of fraud transactions and 36% of fraud-related losses. These schemes rely on human interaction and deception, including messages, links and requests designed to persuade victims to disclose sensitive information or authorize transactions.
Vishing, or voice-based scams, is identified in the source as the most prevalent threat, accounting for more than 21% of reported incidents. Other listed categories include malware and rogue applications at 7.5%, smishing or SMS-based scams at 3%, and phishing emails at 2%.
BPI works with the Philippine National Police Anti-Cybercrime Group (PNP-ACG) and the Department of Information and Communications Technology’s ICT Literacy and Competency Development Bureau (DICT-ILCDB) on cybersecurity awareness and online-fraud concerns. The bank also implements measures under the Anti-Financial Account Scamming Act (AFASA), or Republic Act No. 12010.
Within its mobile app, BPI says it continues to strengthen digital security through several customer-focused safeguards. Mobile Key Authentication replaces traditional SMS one-time passwords with device-based authentication using a PIN and biometrics linked to a trusted device.
Mandatory cool-off periods add a verification window for certain high-risk account changes. According to BPI, the measure can give customers time to detect and report unauthorized activity before transactions are completed.
The app’s integrity checks are intended to identify potentially unsafe environments and restrict access from rooted devices or VPN-enabled environments that may present elevated security risks. Masked Names limit the visibility of personal information during BPI-to-BPI fund transfers while maintaining transaction transparency and security.
These BPI digital banking security safeguards address technical and privacy risks, but the bank also emphasizes customer awareness. Fitz Chee, BPI’s Head of Consumer Platforms, said customers need to understand risks and feel confident making decisions online.
“Making digital banking safer is not just about the technology behind it. Customers also need to understand the risks and feel confident making decisions online. When people know how to recognize suspicious activity and take the right precautions, they are better equipped to protect themselves. Building that awareness is an important part of helping more people bank digitally with confidence,” Chee said.
BPI’s BPI digital banking security program therefore combines app-based controls, fraud-awareness efforts and coordination with government and law-enforcement bodies. The source does not specify new product availability, pricing or additional customer eligibility conditions tied to the listed safeguards.